Completed Case Study
ENVELOPE DFIR: Malware & Incident Response
A Windows incident response and malware analysis write-up covering phishing, shortcut execution, PowerShell, persistence, DLL side-loading, live C2 validation, and detection engineering.
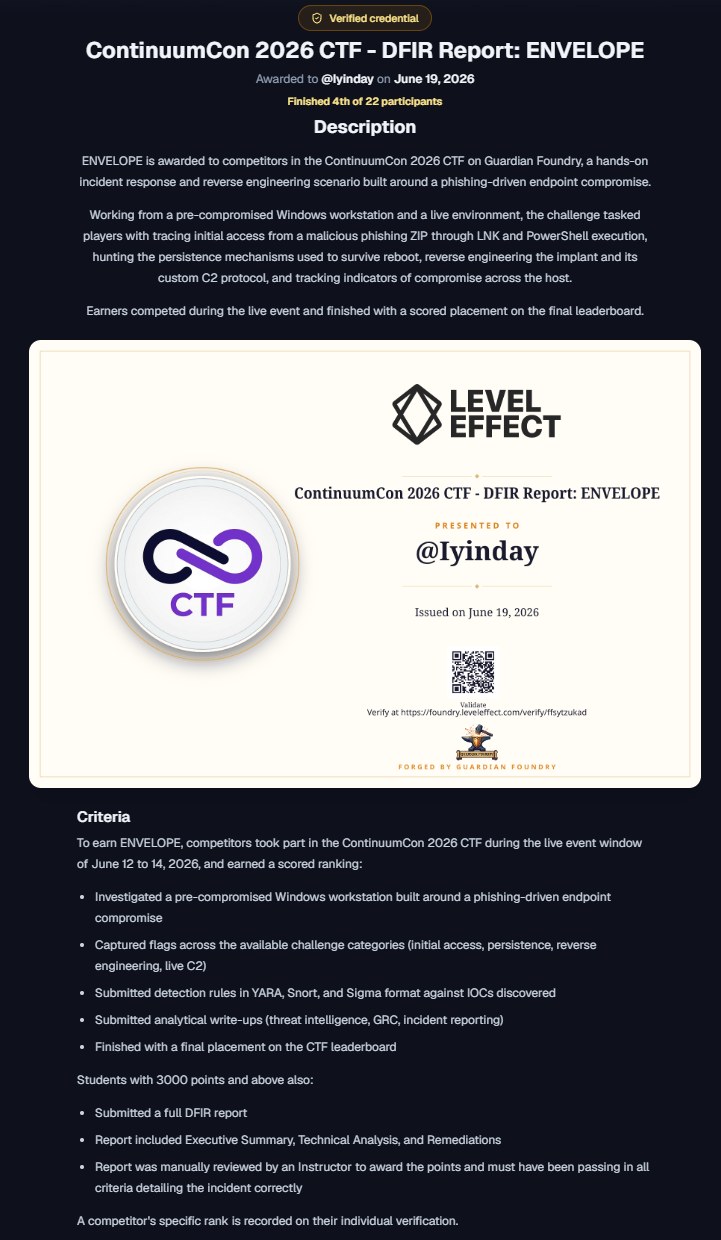
Objective
Trace how a phishing-led compromise executed, identify staged payloads, validate persistence and C2 behavior, recover key evidence, and document defensive lessons.
Work performed
Reviewed shortcut behavior, decoded Base64-wrapped PowerShell, identified XOR payload decoding, examined staged files, analyzed persistence through scheduled tasks and WMI, and documented C2 interaction.
Skills demonstrated
Windows DFIR, PowerShell analysis, malware triage, persistence review, YARA/Sigma rule writing, MITRE ATT&CK mapping, C2 analysis, remediation planning, and report writing.
Outcome
Created a full portfolio lab report showing commands, outputs, findings, detection rules, severity reasoning, remediation steps, and final incident summary.