Hello, I’m Ayinde Perouza
Building Secure IT Foundations for Cybersecurity Operations
I bridge enterprise IT support and cybersecurity operations by turning systems administration, identity and access management, endpoint support, and troubleshooting experience into practical security outcomes.
Solving / researching: how secure administration, identity controls, endpoint telemetry, and detection workflows can help analysts investigate incidents faster and document defensible findings.
Enterprise IT • Systems Administration • Cybersecurity Operations
Currently building practical skills in SOC triage
About
Practical IT operations experience with a strong cybersecurity direction.
I bring practical experience supporting enterprise users across multiple business units in fast-paced, SLA-driven environments, with a focus on reliable service delivery, secure operations, clear documentation, and continuous professional development.
My cybersecurity growth is built through hands-on labs, CTF investigations, packet analysis, Windows and Linux administration, detection logic, and evidence-based reporting. I focus on validating findings, documenting what happened, and connecting technical activity to business risk.
Core Skills
Skills aligned to IT operations, security operations, and infrastructure support.
Cybersecurity Operations
Alert review, SOC triage, IOC documentation, MITRE ATT&CK mapping, escalation notes, and evidence-based reporting.
Systems, Identity & Access
Windows Server, Linux administration, Active Directory, DNS/DHCP, Group Policy, Microsoft Entra ID, Microsoft 365, onboarding/offboarding, and least-privilege support.
Endpoint, Network & Traffic Analysis
Microsoft Defender, endpoint security review, Wireshark, PCAP analysis, TCP/IP, DNS/HTTP investigation, firewall concepts, VPN concepts, and segmentation awareness.
Security Tools & Documentation
Wazuh, Splunk, Security Onion, Elastic/Kibana, PowerShell, Linux CLI, VMware Workstation, YARA/Sigma/Snort-style logic, technical reports, and case-study documentation.
Featured Projects
Selected labs, case studies, and verified skill work.
Use the dropdown arrows to expand details, or open the full project archive for the complete list.
 Completed
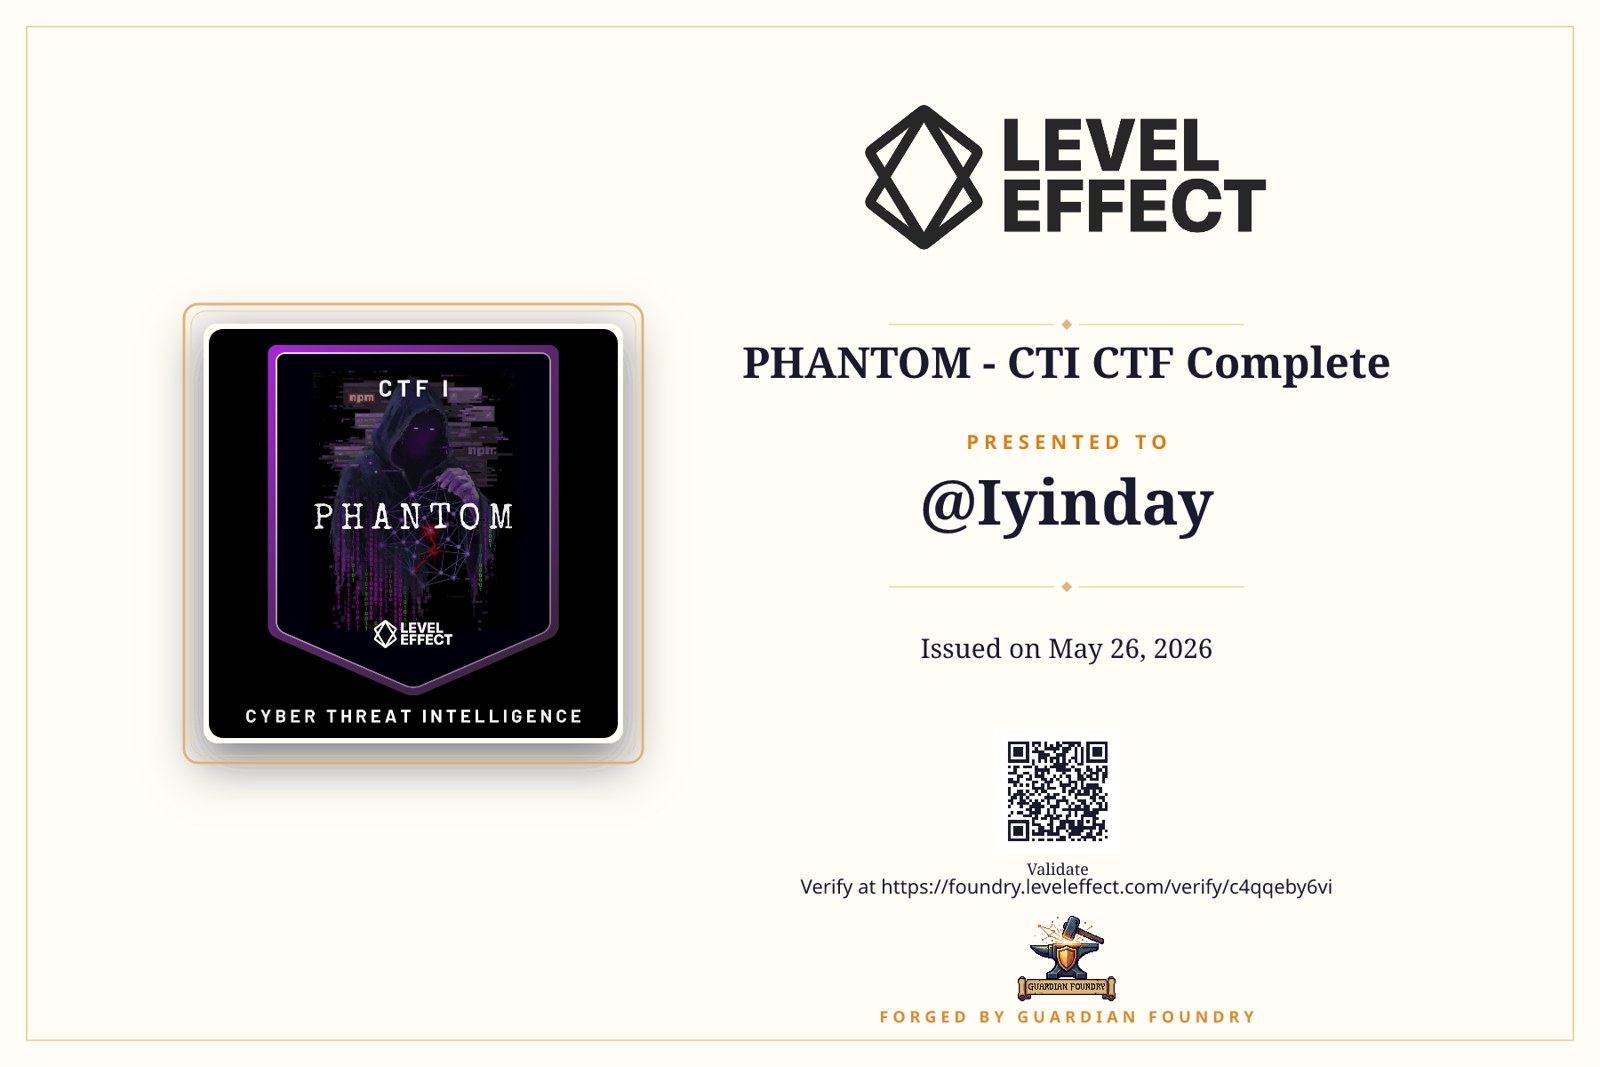
PHANTOM CTI CTF: Supply Chain Investigation
Investigated a simulated npm supply-chain compromise affecting a GitHub Actions self-hosted runner, including IOC extraction, MITRE mapping, threat hunting, and detection logic.
PHANTOM CTI CTF: Supply Chain Investigation
Investigated a simulated npm supply-chain compromise affecting a GitHub Actions self-hosted runner, including IOC extraction, MITRE mapping, threat hunting, and detection logic.
Built an evidence-based investigation narrative from package-lock changes, CI/CD logs, proxy evidence, GitHub audit activity, malware behavior, indicators of compromise, and remediation priorities.
 Completed
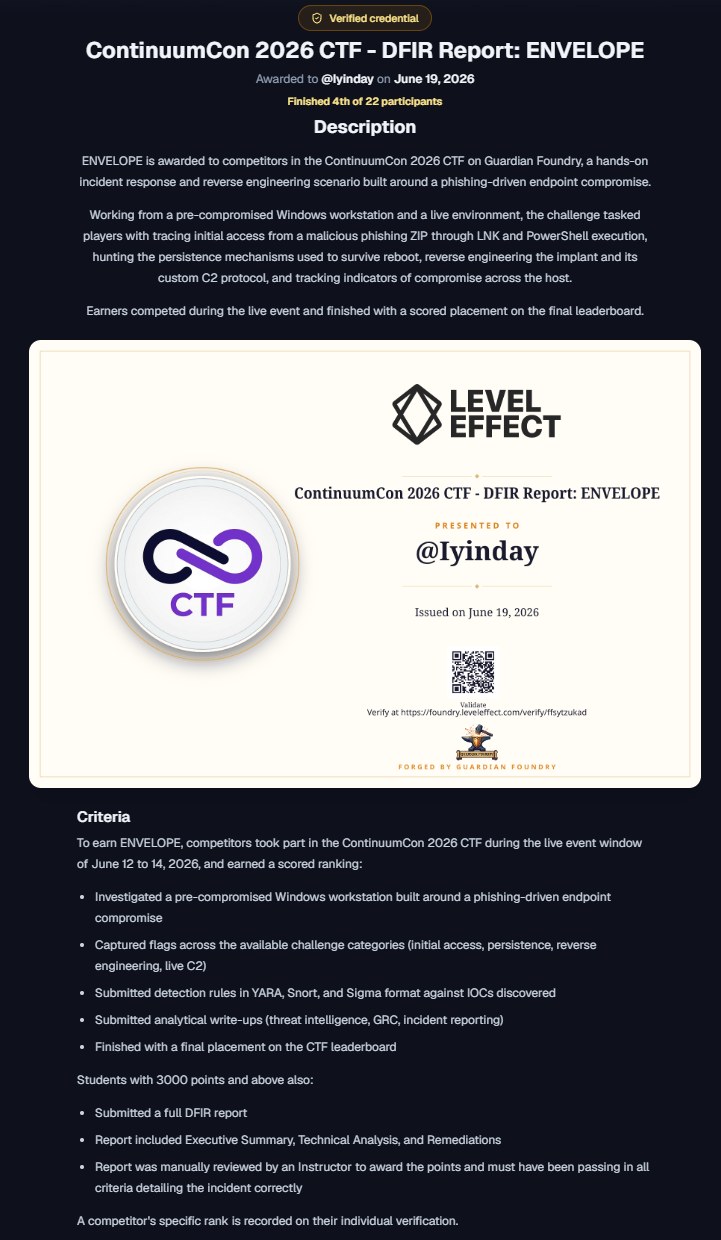
ENVELOPE DFIR: Malware & Incident Response
Documented a phishing-led Windows compromise involving PowerShell, persistence, DLL side-loading, live C2 interaction, credential material, and detection engineering.
ENVELOPE DFIR: Malware & Incident Response
Documented a phishing-led Windows compromise involving PowerShell, persistence, DLL side-loading, live C2 interaction, credential material, and detection engineering.
Reviewed Windows artifacts, decoded payload behavior, mapped persistence mechanisms, identified high-fidelity detection signals, and produced remediation recommendations for a lab incident scenario.
 Completed
Build a SOC Lab with Wazuh | AI-Assisted SOC Triage
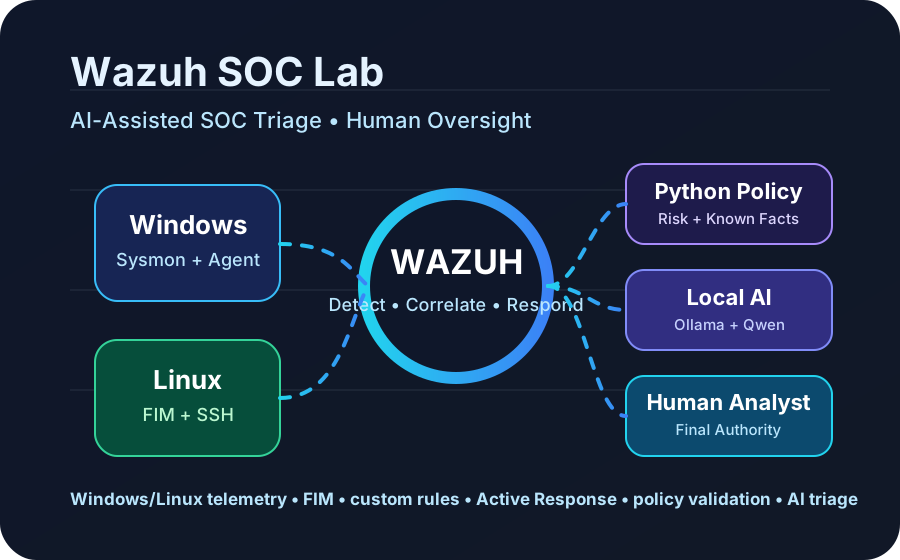
Built a Wazuh SOC lab with Windows/Linux telemetry, FIM, custom rules, dashboards, Active Response, and a local AI-assisted triage extension using Ollama, Qwen, Python policy logic, and human validation.
Build a SOC Lab with Wazuh | AI-Assisted SOC Triage
Built a Wazuh SOC lab with Windows/Linux telemetry, FIM, custom rules, dashboards, Active Response, and a local AI-assisted triage extension using Ollama, Qwen, Python policy logic, and human validation.
Extended a traditional SIEM monitoring lab into a hybrid SOC workflow where Wazuh detects, Python enforces known facts, AI explains and recommends, and the human analyst remains the final decision authority.
 Completed
AI Phishing Email Analyzer
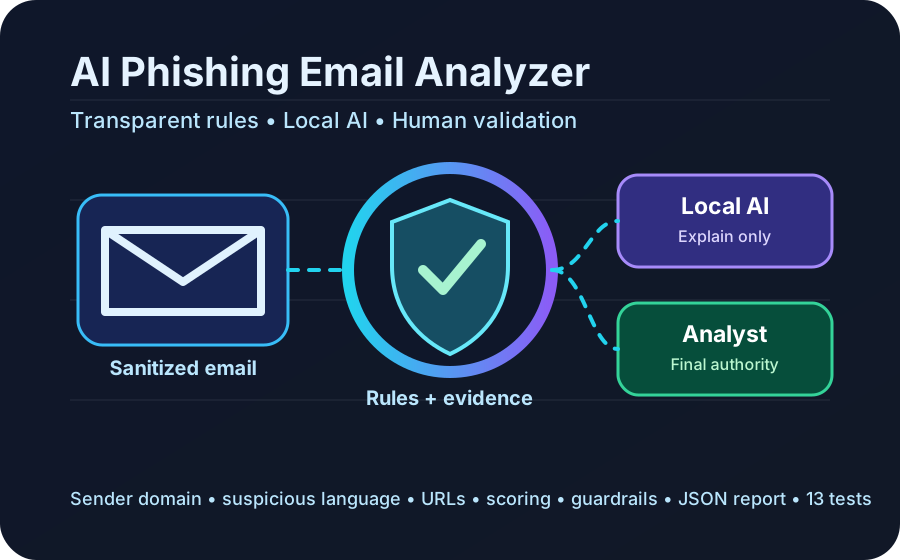
Built a transparent phishing-analysis application with Python, Streamlit, optional local Ollama and Qwen explanations, guardrails, JSON reporting, and 13 automated tests.
AI Phishing Email Analyzer
Built a transparent phishing-analysis application with Python, Streamlit, optional local Ollama and Qwen explanations, guardrails, JSON reporting, and 13 automated tests.
Detection Engine v2 corrected three false negatives through expanded social-engineering rules, multiline header parsing, sender-domain extraction, and brand-domain validation while Python retained control of the evidence, score, and classification.
 Completed
Ubuntu Application Server Secure Baseline & Recovery
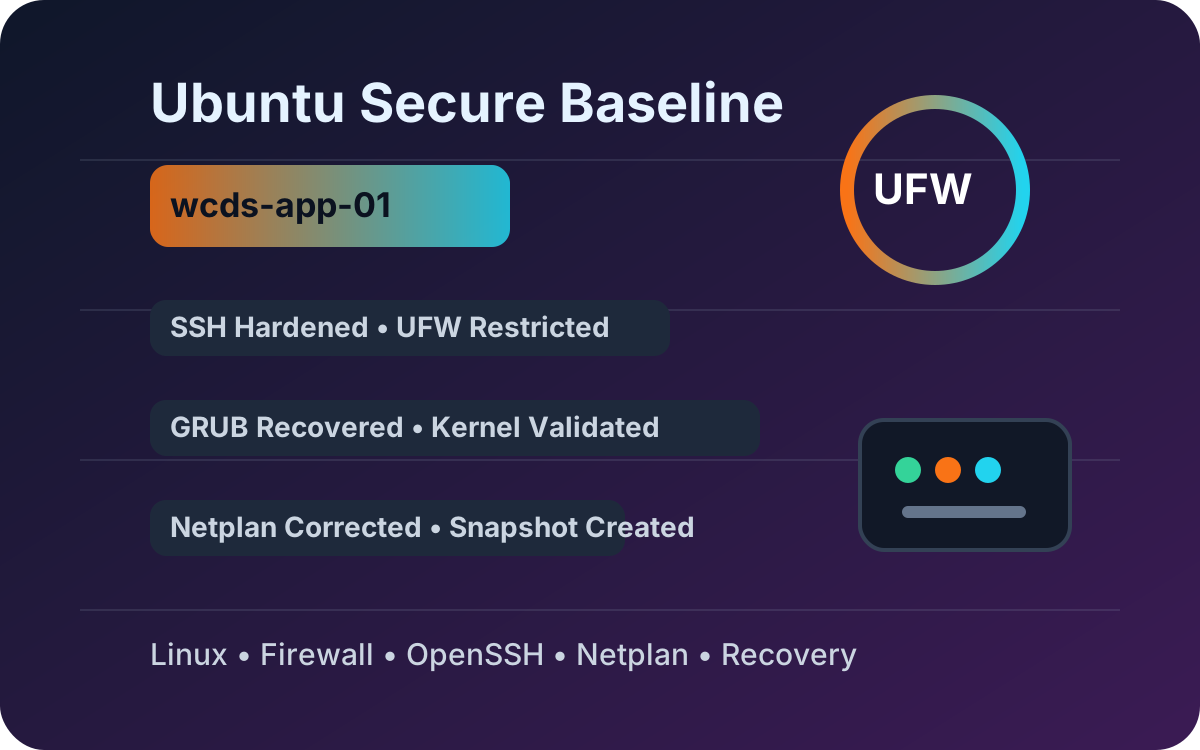
Hardened an Ubuntu 24.04 application server in a VMware lab, including package repository repair, GRUB recovery, UFW firewall restriction, OpenSSH hardening, Netplan correction, and recovery snapshots.
Ubuntu Application Server Secure Baseline & Recovery
Hardened an Ubuntu 24.04 application server in a VMware lab, including package repository repair, GRUB recovery, UFW firewall restriction, OpenSSH hardening, Netplan correction, and recovery snapshots.
Documented a repeatable Linux infrastructure-security baseline for wcds-app-01, validated DNS, routing, TLS reachability, package health, SSH service status, firewall scope, and zero failed systemd units.
 Completed
Cyber Defense Technician Practical Path
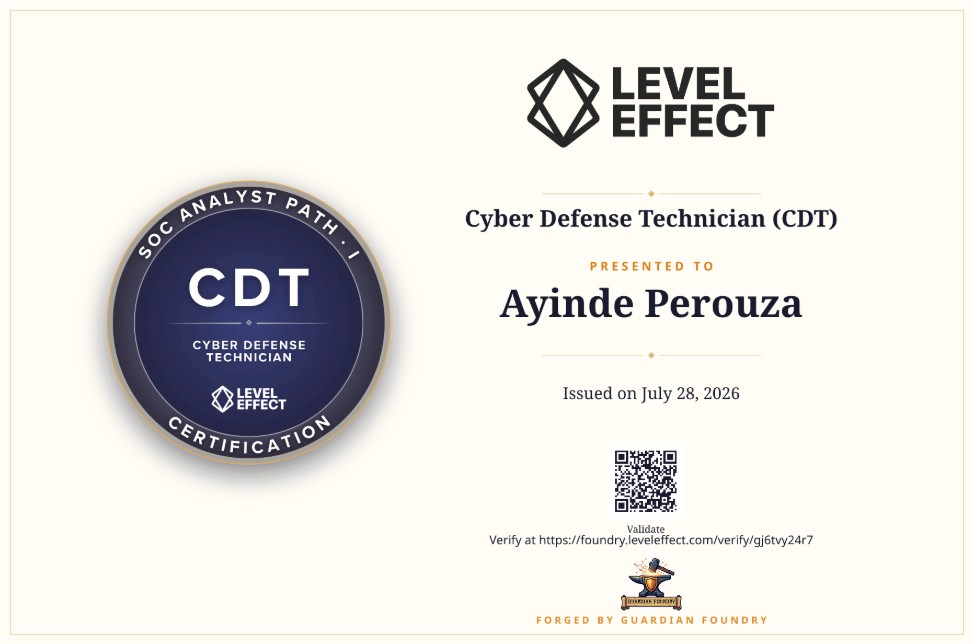
Summarized a hands-on Level Effect path covering Windows, Linux, networking, Active Directory, helpdesk ticket handling, evidence review, and the CDT scenario-based exam.
Cyber Defense Technician Practical Path
Summarized a hands-on Level Effect path covering Windows, Linux, networking, Active Directory, helpdesk ticket handling, evidence review, and the CDT scenario-based exam.
This path connects IT operations fundamentals to the SOC Analyst Path by building practical Windows, Linux, network, Active Directory, troubleshooting, and evidence-based decision-making skills.
 Completed
Windows Enterprise Administration & Active Directory Security Lab
Consolidated Windows Server and Active Directory lab covering AD DS, DNS/DHCP, Group Policy, forest trusts, delegated administration, file services recovery, PowerShell, and security validation.
Windows Enterprise Administration & Active Directory Security Lab
Consolidated Windows Server and Active Directory lab covering AD DS, DNS/DHCP, Group Policy, forest trusts, delegated administration, file services recovery, PowerShell, and security validation.
Documented end-to-end administration, troubleshooting, remediation, and validation across a controlled enterprise-style lab, including TT.WI.LOCAL, BB.WI.LOCAL, and a separate GOODCORP least-privilege delegation challenge.
 Completed
Cybersecurity Portfolio Rebuild
Rebuilt an early front-end portfolio into a focused IT and cybersecurity portfolio with case studies, responsive layout, project archive, theme toggle, and animated UI elements.
Cybersecurity Portfolio Rebuild
Rebuilt an early front-end portfolio into a focused IT and cybersecurity portfolio with case studies, responsive layout, project archive, theme toggle, and animated UI elements.
Turned the portfolio itself into a documented project covering content strategy, responsive front-end design, accessibility, dark/light mode, collapsible project cards, and public-safe presentation.
Education, Certifications & Training
Formal education, completed certifications, and targeted technical training.
BSc in Computer Science
London Metropolitan University | 2022
Cyber Defense Technician (CDT) - 2026
Level Effect Guardian Foundry credential covering Windows, Linux, networking fundamentals, system administration, Active Directory, helpdesk ticket handling, and evidence-based exam scenarios.
View verified skill sheetFortinet Certified Associate in Cybersecurity - 2025
Security awareness and Fortinet ecosystem fundamentals.
Google Cybersecurity Professional Certificate - 2024
Security operations, SIEM concepts, Linux, SQL, Python basics, and incident response fundamentals.
Microsoft Azure Fundamentals - Internal Training - 2024
Foundational exposure to Azure services, cloud concepts, security, governance, and administration.
ISC2 Certified in Cybersecurity (CC) - 2023
Foundational security principles, access control, network security, and security operations.
EC-Council Network Defence Essentials (NDE) - 2023
Network defense concepts, monitoring awareness, and defensive fundamentals.
Community & Platforms
Places where I continue learning, practicing, and building evidence.
Level Effect / Guardian FoundryGuardian Foundry badge and verified skill-sheet record.
Level Effect Skill SheetBadge and skills record for completed Guardian Foundry work.
TryHackMeHands-on cybersecurity practice and learning rooms.
StationXCybersecurity training and skills development.
TechTwoFortyTraining interest area: cloud-security engineering pathway.
Contact
Let’s Connect
Interested in discussing IT support, cybersecurity projects, SOC work, infrastructure security, technical documentation, or collaboration opportunities?
I’m open to connecting with teams, mentors, recruiters, and peers who value practical technical work, clear documentation, and continuous development.